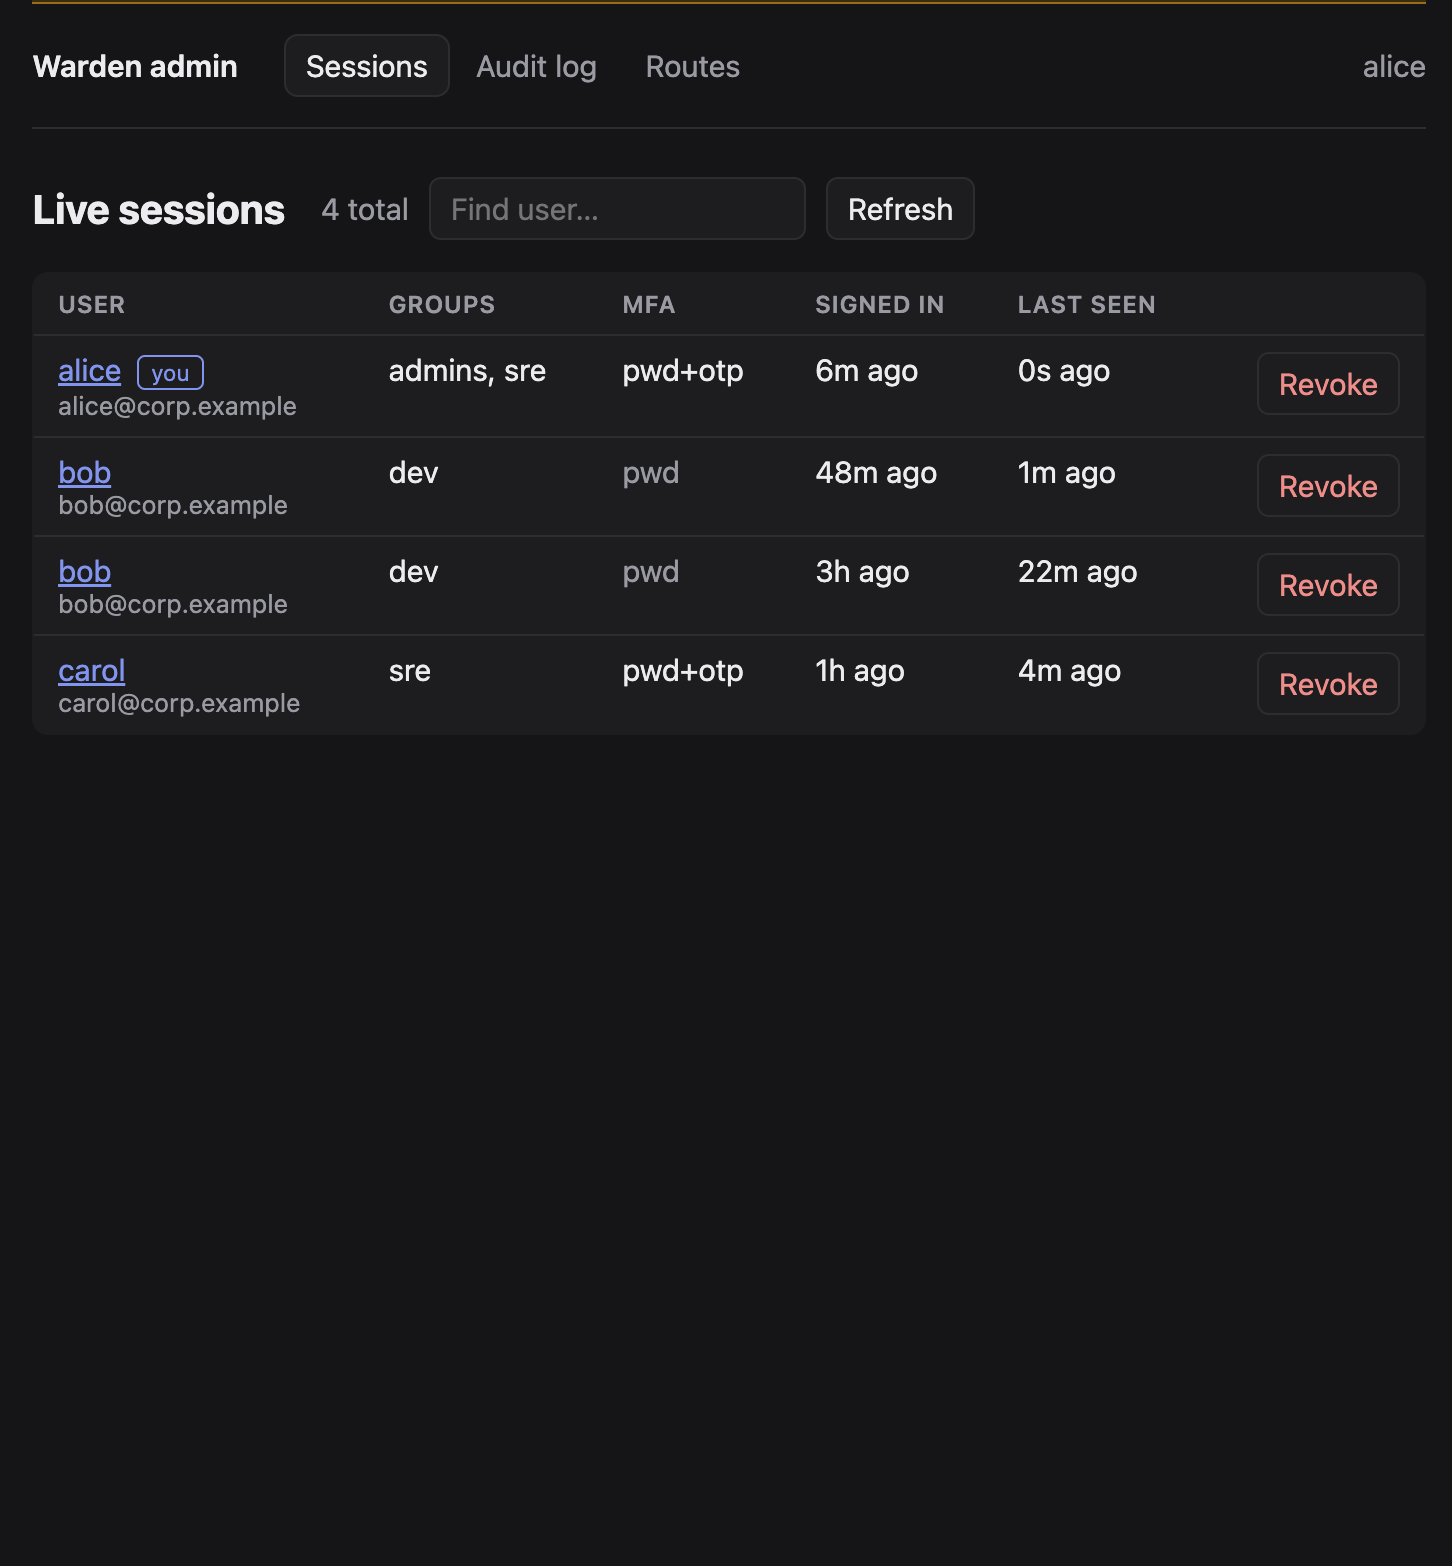
01Warden
- Go
- OAuth 2.0 / OIDC
- Keycloak
- Redis
- Docker
A zero-trust reverse proxy in Go that checks every request before it reaches an internal app: who you are, whether you're allowed on that exact path, and whether your session is still valid. Authentication runs through OIDC with PKCE against Keycloak, path policies default to deny, and every decision is written to an audit log. Sessions live in Redis so they can be revoked server-side immediately instead of waiting out a token expiry.